Managed IT Services
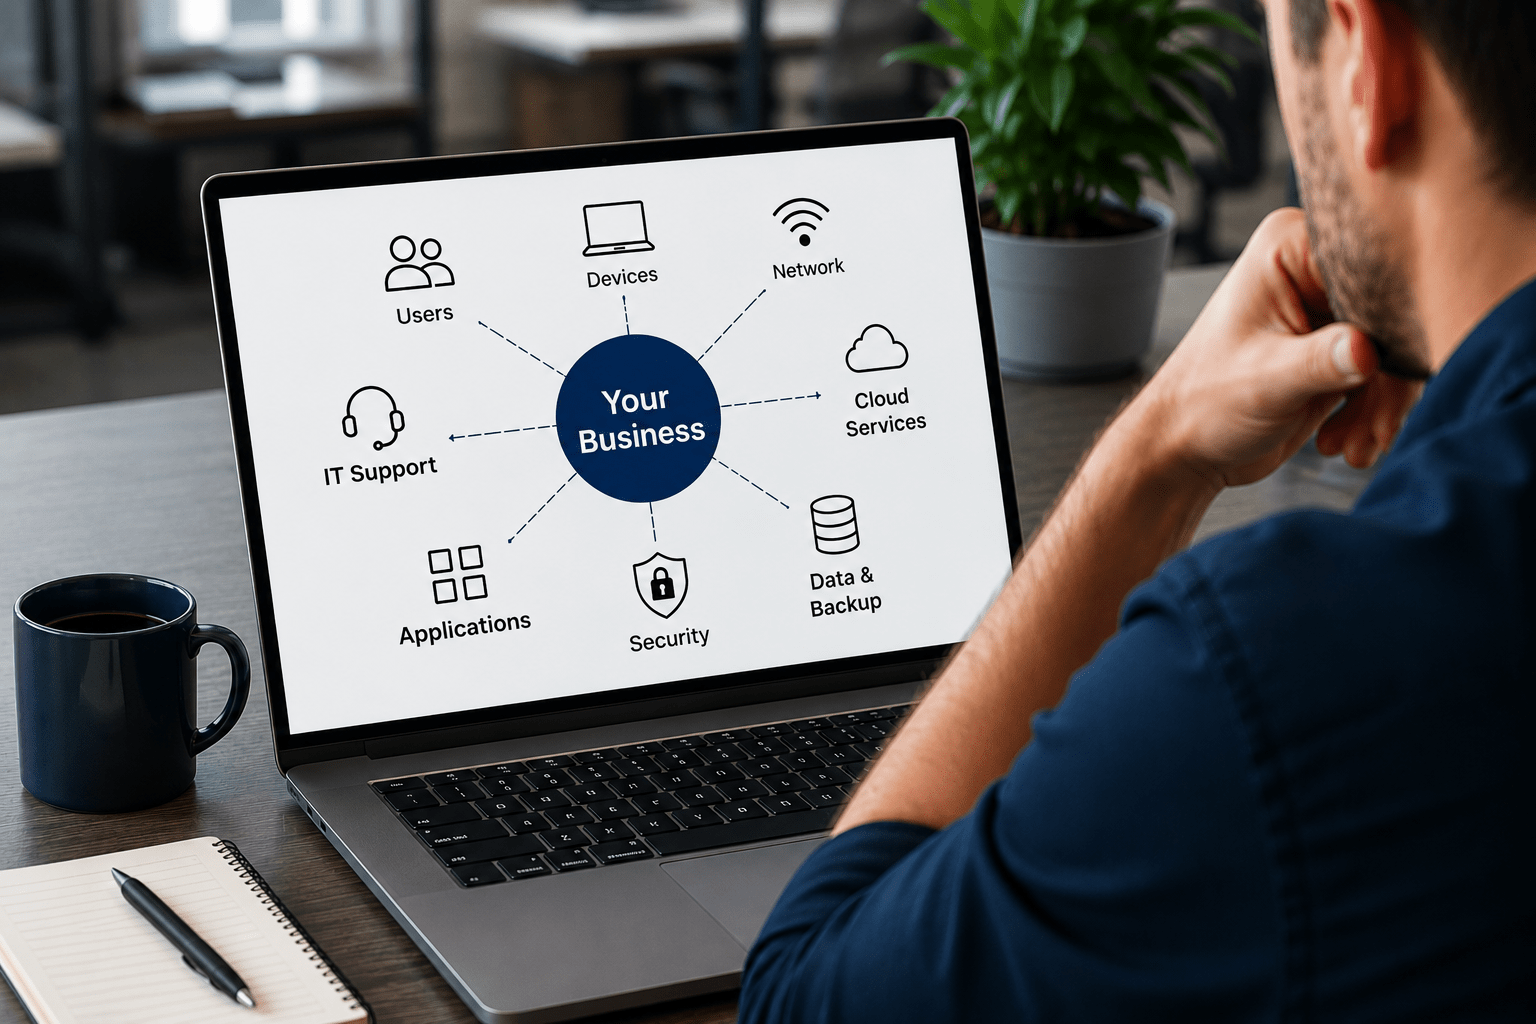
Our Managed IT Services are built on security and partnership. We work with forward-thinking businesses, helping them manage and secure their workplace in line with frameworks such as NIS2, DORA and ISO 27001, with the evidence to prove it. We are Microsoft-first, with deep expertise in Microsoft 365, Azure and Azure Virtual Desktop.
All of our partnerships start with an assessment to establish a secure baseline, ensuring we have a thorough understanding of your IT and are fully aligned on your business priorities.
Four Key Services
WORKFORCE 365
Microsoft 365
Identity, endpoints, data, collaboration
- Entra ID, conditional access and MFA
- Intune device management and compliance
- Purview data protection and governance
- Email security and collaboration controls
- Licensing optimisation
AZURE IGNITE
Microsoft Azure
Landing zones, workload security, cost control
- Landing zone design and build
- Infrastructure-as-code and policy
- Workload and network security
- Defender for Cloud monitoring
- Cost governance and FinOps reporting
AVD CONTINUUM
Desktop
Azure Virtual Desktop, done at scale
- Hardened golden images and patching
- Profile, session and scaling management
- Access control and data-egress restriction
- Capacity that flexes with headcount
- Citrix and VMware replacement
AZURITE FOCUS
& Strategy
Roadmap, risk, budget, board-ready reporting
- Three-year roadmap and quarterly business reviews
- Budget planning, licence and cost modelling
- Standing risk and recommendations register
- Vendor oversight and rationalisation
- Board-ready reporting in plain business terms
All services
Cyber Security & SOC
24/7 managed detection and response across identity, endpoint and cloud. MDR, EDR, XDR and SIEM, triaged and contained by people.
IT Support & Service Desk
Engineers who know your environment, working to written response and resolution targets you can hold us to.
Backup & Disaster Recovery
Protected, immutable copies of the data that matters, with restores tested on a schedule and recovery times you have agreed.
Monitoring & Patching
Availability, capacity and configuration watched continuously, so the first person who knows something changed is us.
Vulnerability Management
Continuous discovery across the estate, risk-ranked against your business, with remediation scheduled and closed out.
Compliance & Audit Support
ISO 27001, NIS2 and DORA. Control mapping, evidence packs, and the documentation auditors and insurers ask for.
Security Awareness Training
Phishing simulation and role-appropriate training, tracked and reported, so the human layer is measured like every other control.
Professional Services
Migrations, tenant consolidation, M&A integration and defined build projects, scoped to an outcome with a fixed end point.
Supply Chain Risk
Supplier assessment and monitoring against the standards you answer to, because NIS2 makes your vendors’ security your problem.
Licensing & Procurement
Microsoft and third-party licensing, hardware sourcing and lifecycle. The right SKUs at the right count, reviewed rather than renewed on autopilot.
Networking & Connectivity
Firewalls, secure access, wireless and site connectivity, designed and managed as part of the security baseline rather than beside it.
AI Enablement & Governance
Copilot and AI tooling deployed with the guardrails first, so productivity gains don’t arrive with a data-leakage problem attached.
How we work
Every engagement runs the same way. We start by understanding where you are and where you’re trying to get to, then work in a clear sequence from there.
Assess. Align. Manage. Advise.
STAGE ONE
Assess
We assess where your technology stands, where the risks are, and what your regulations and risk appetite require. From that we define the secure baseline your business needs.
STAGE TWO
Align
This is where the implementation begins. We bring your environment up to the agreed baseline and align it with your business roadmap.
STAGE THREE
Manage
Ongoing management, monitoring and support, so the baseline holds and configuration doesn’t drift. When something real changes, a new regulation, an acquisition, a genuine shift in risk, we revisit it.
STAGE FOUR
Advise
Quarterly business reviews, a technology roadmap, licence and cost modelling, and a standing risks and recommendations register that is reviewed and re-prioritised, never closed.
We help you align your environment to the standards your business requires, such as ISO 27001, NIS2 and DORA, and we keep the evidence that proves it. When an auditor, a client’s security questionnaire, or a cyber insurance form asks how you handle something, the answer is a report we can produce, not a scramble to assemble one.
The IT Sanity Check
Does your IT environment cover all the bases?
We have prepared fourteen quick questions to help you sanity-check your IT. You’ll get a written reflection back: what’s solid, what’s exposed, where to look next.